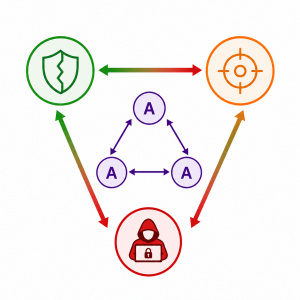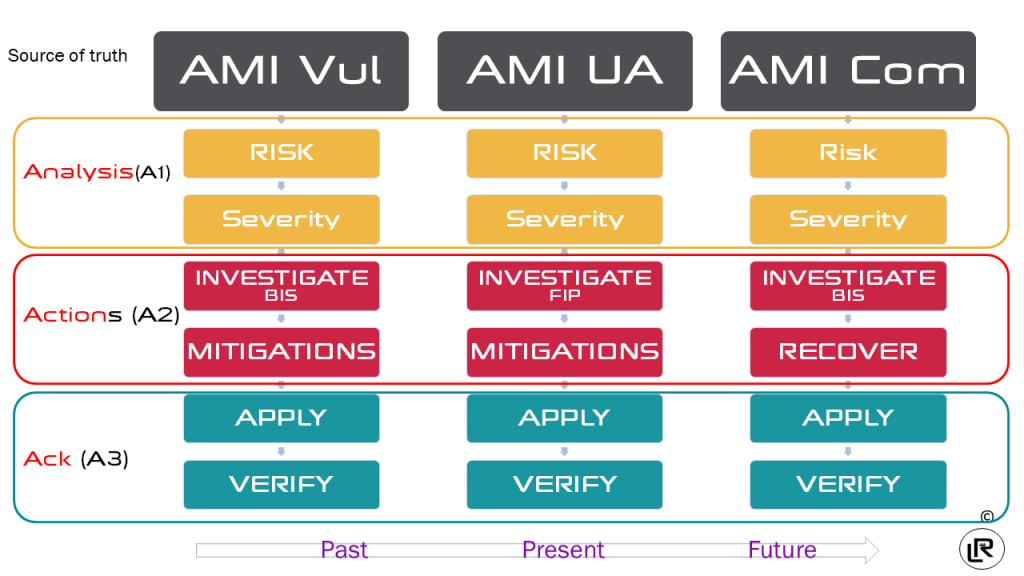
AMI3A is a simple decision framework that helps security teams determine where they are in the security lifecycle and what actions to take next.
The Three Core Questions
- Am I Vulnerable? (AmiVul)
- What weaknesses exist?
- How likely are they to be exploited?
- What is the business risk?
- Focus: Exposure reduction and prevention.
- Am I Under Attack? (AmiUA)
- Is an attack happening now?
- What is the attacker doing?
- How do we detect, mitigate, and stop it?
- Focus: Real-time defense and incident response.
- Am I Compromised? (AmiComp)
- Has the attacker succeeded?
- What assets, data, or systems were affected?
- What is the business impact and recovery path?
- Focus: Containment, eradication, and recovery.
The Security Timeline : Past Present Future
Potential → Attack → Compromise
AmiVul → Prevent
AmiUA → Defend
AmiComp → Recover
Execution Engine (AAA)
For each AMI state:
Analyze → Action → Acknowledge
- Analyze the situation
- Take corrective action
- Confirm the result
SIRT Mapping
| Function | AMI State |
| PSIRT | AmiVul |
| CSIRT | AmiUA |
| Incident Recovery / DFIR | AmiComp |
One-Sentence Definition
AMI3A is a security decision model that helps organizations determine whether they are vulnerable, under attack, or compromised, and provides a structured path for prevention, defense, and recovery.